Security

Security built into every XFIV product

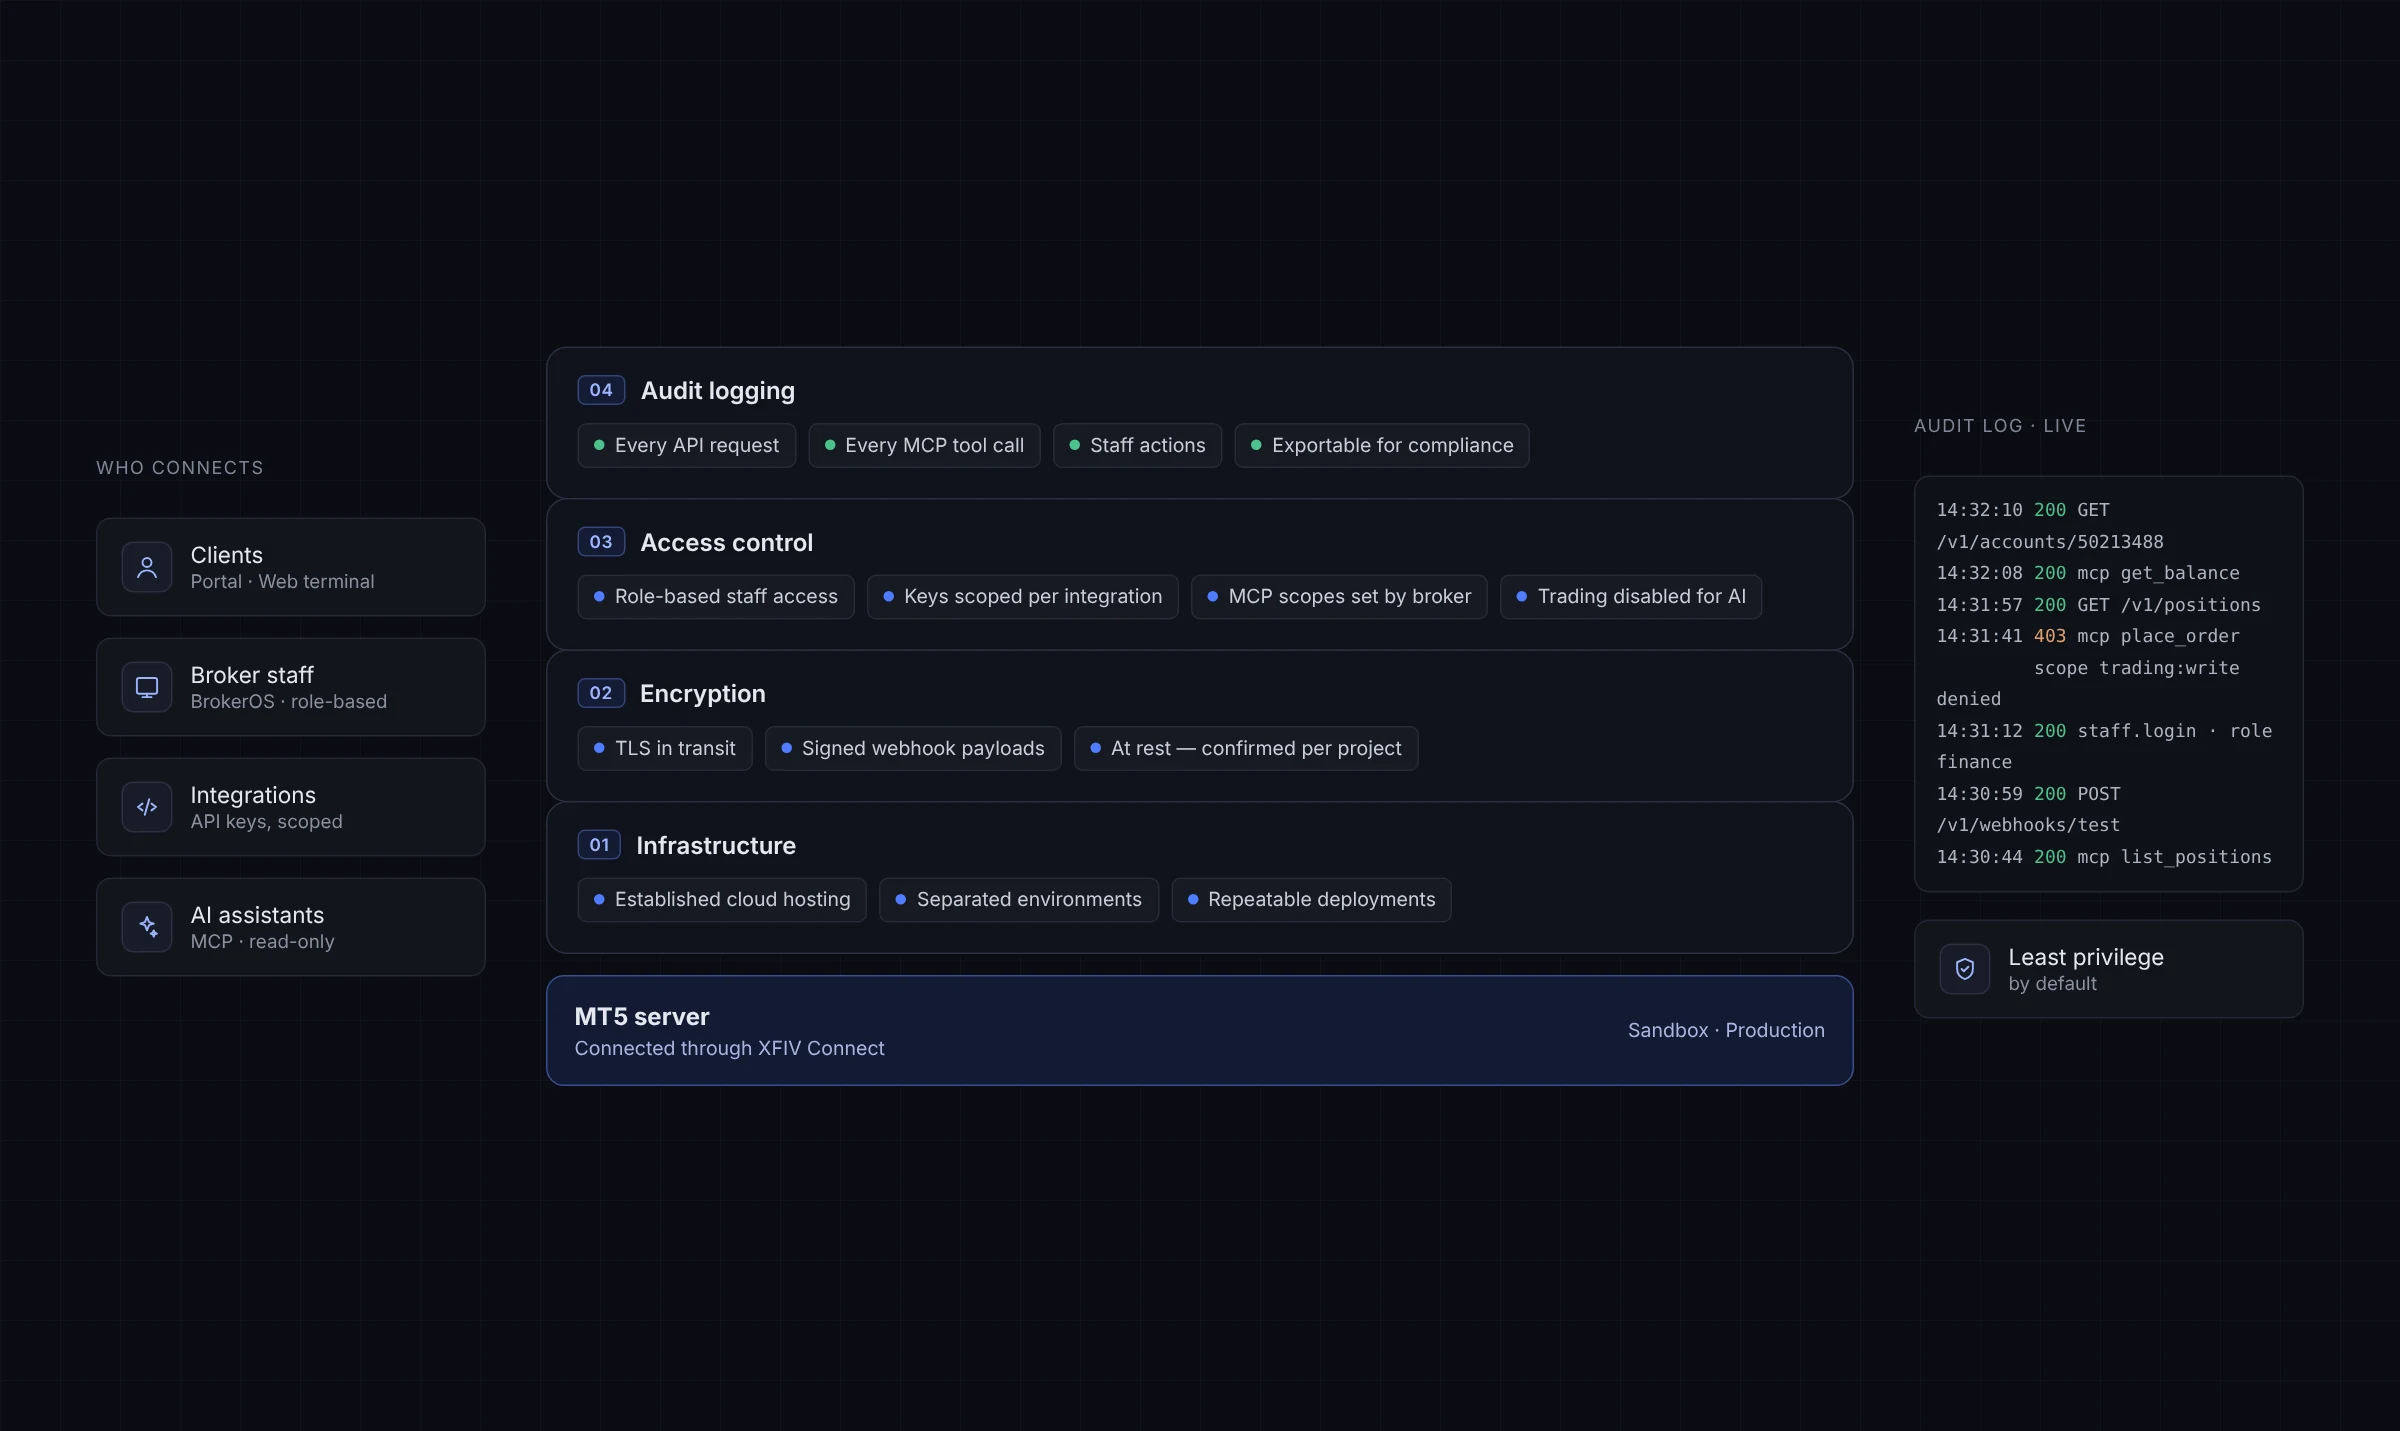
XFIV security starts with the basics done properly. Access is role-based, API keys are scoped per integration, and every API and MCP request is written to an audit log. AI assistants get read-only, broker-scoped access and cannot place trades. Hosting and data-protection details are shared during your security review.

Diagram of XFIV security layers: infrastructure, encryption, access control and audit logs
Infrastructure

Infrastructure designed for separation

XFIV products are designed to run on established cloud infrastructure, with our own controls on top and consistent, repeatable deployments. Hosting details are confirmed per project.

  • Cloud-hosted infrastructure
  • Backups designed into the platform
  • Sandbox and production designed to be separate
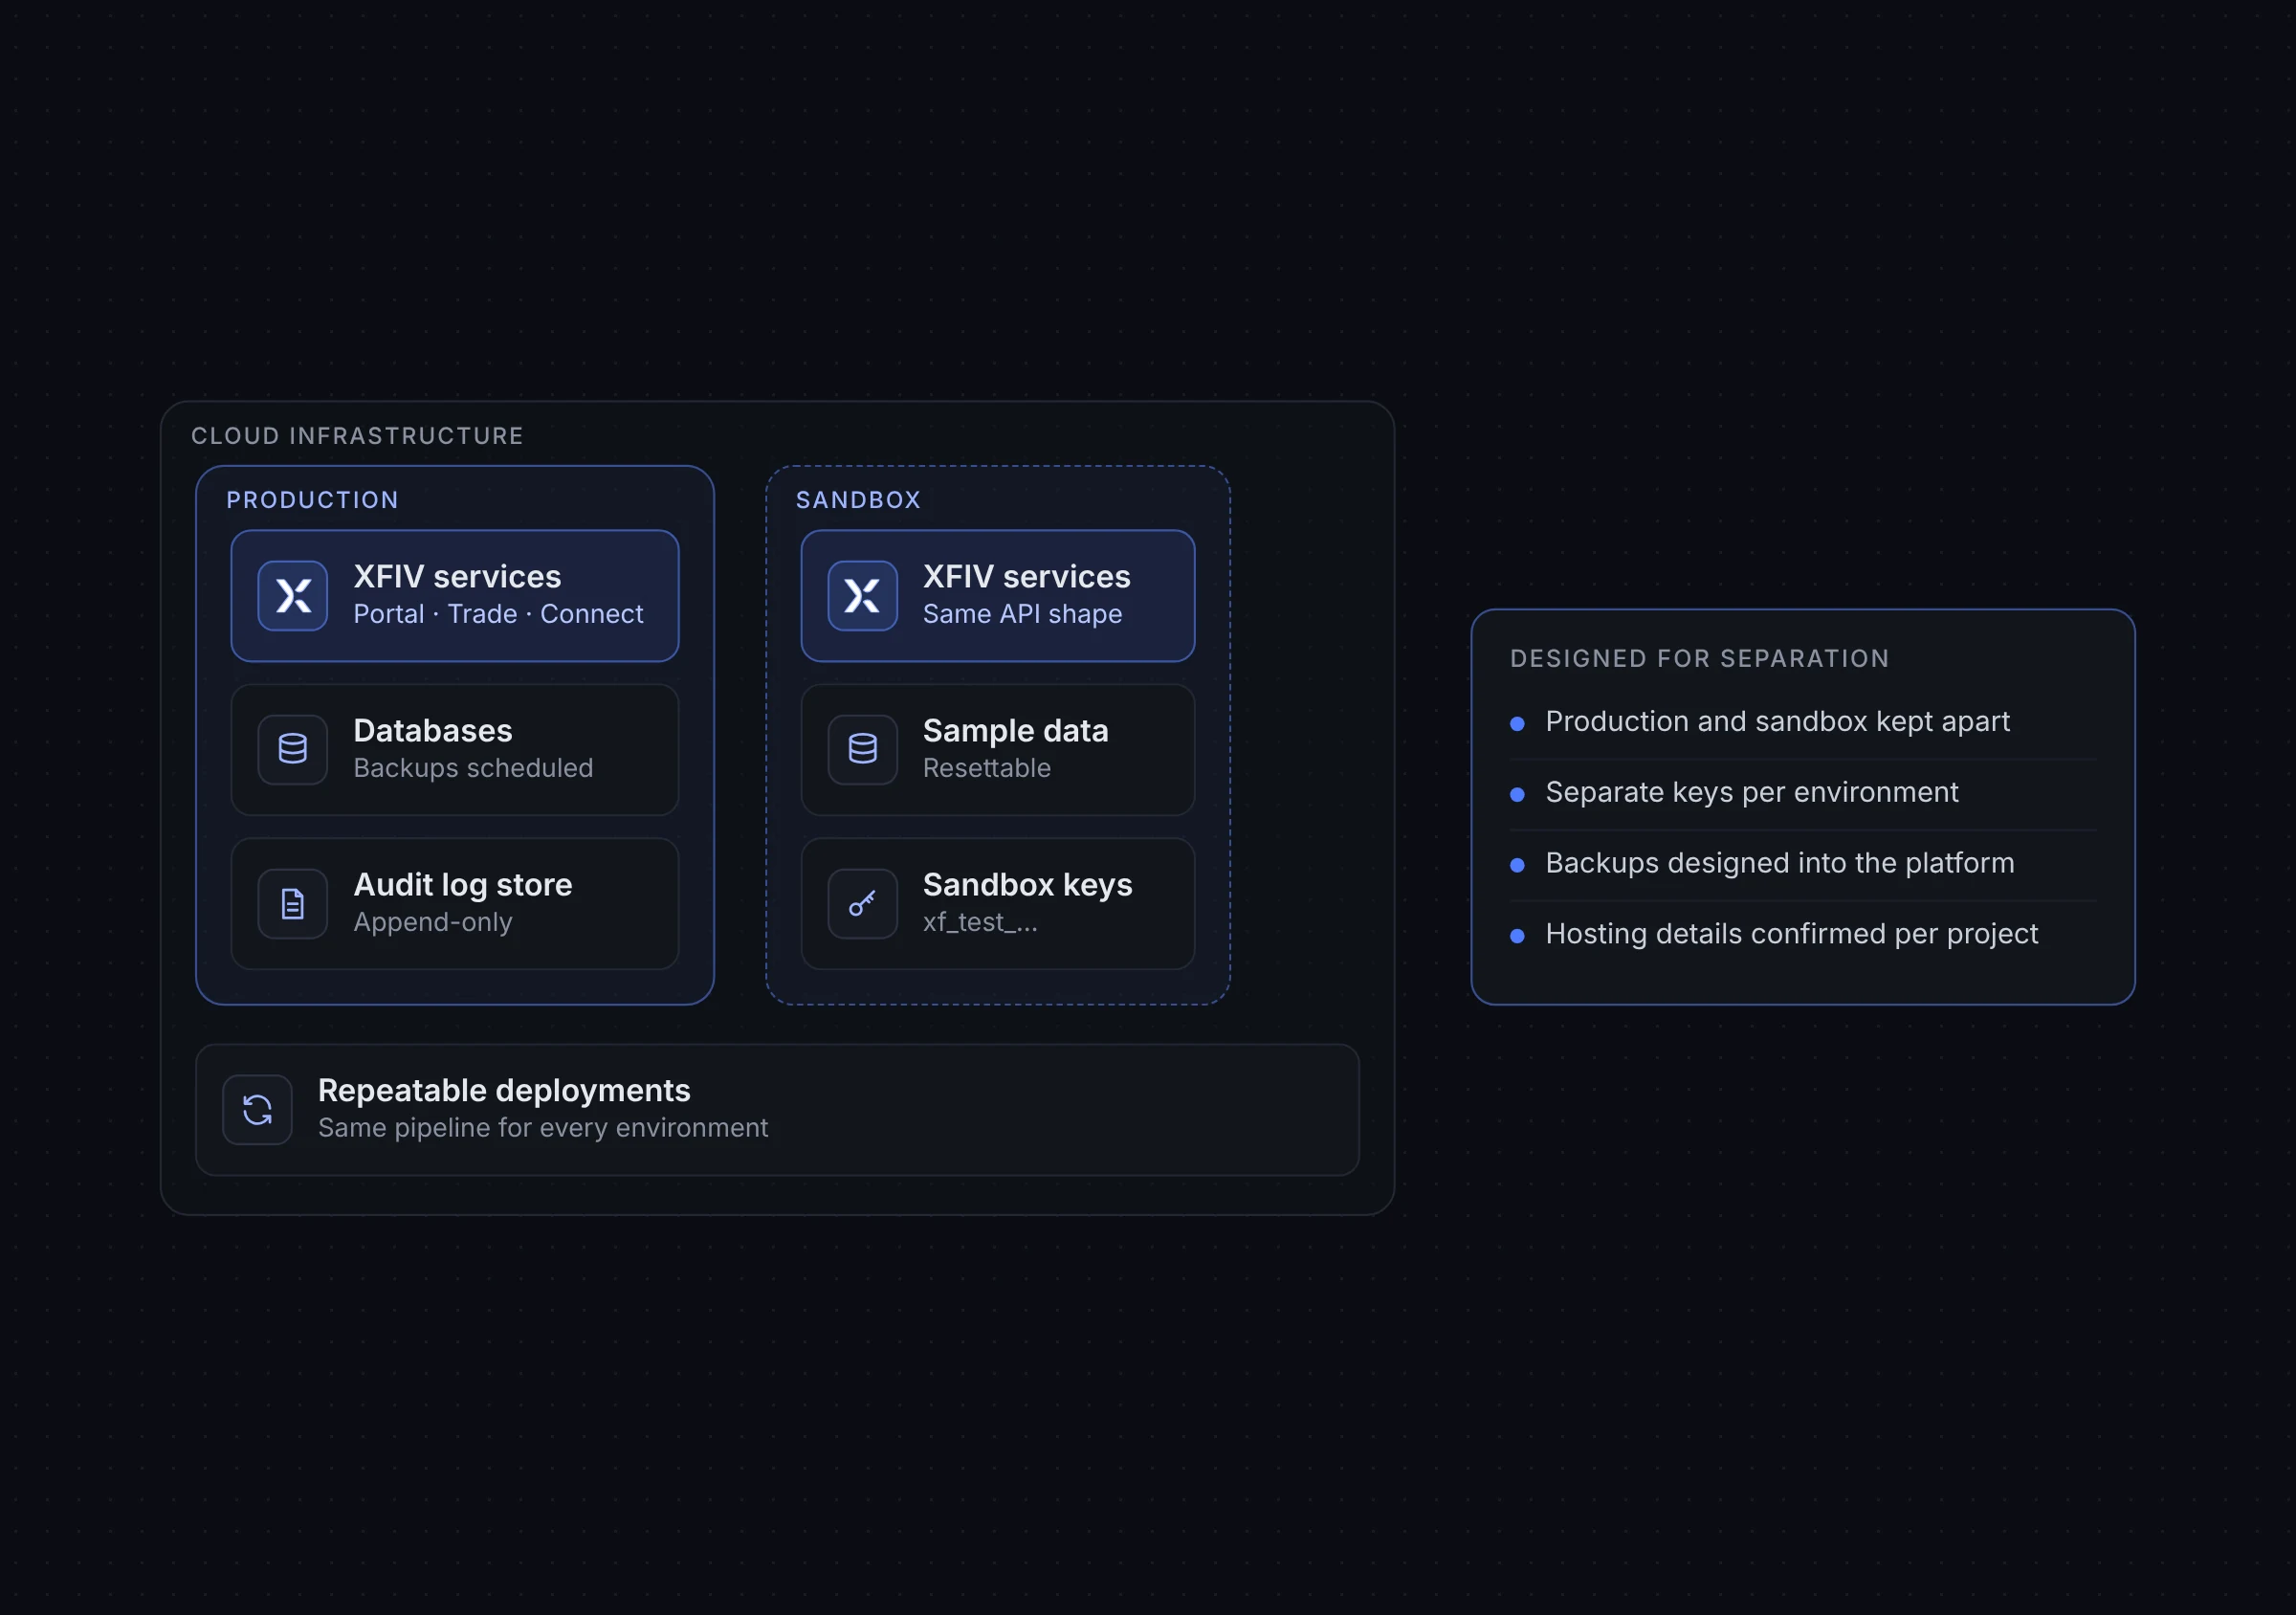
Infrastructure diagram with XFIV services running on cloud infrastructure
Encryption

Encryption in transit

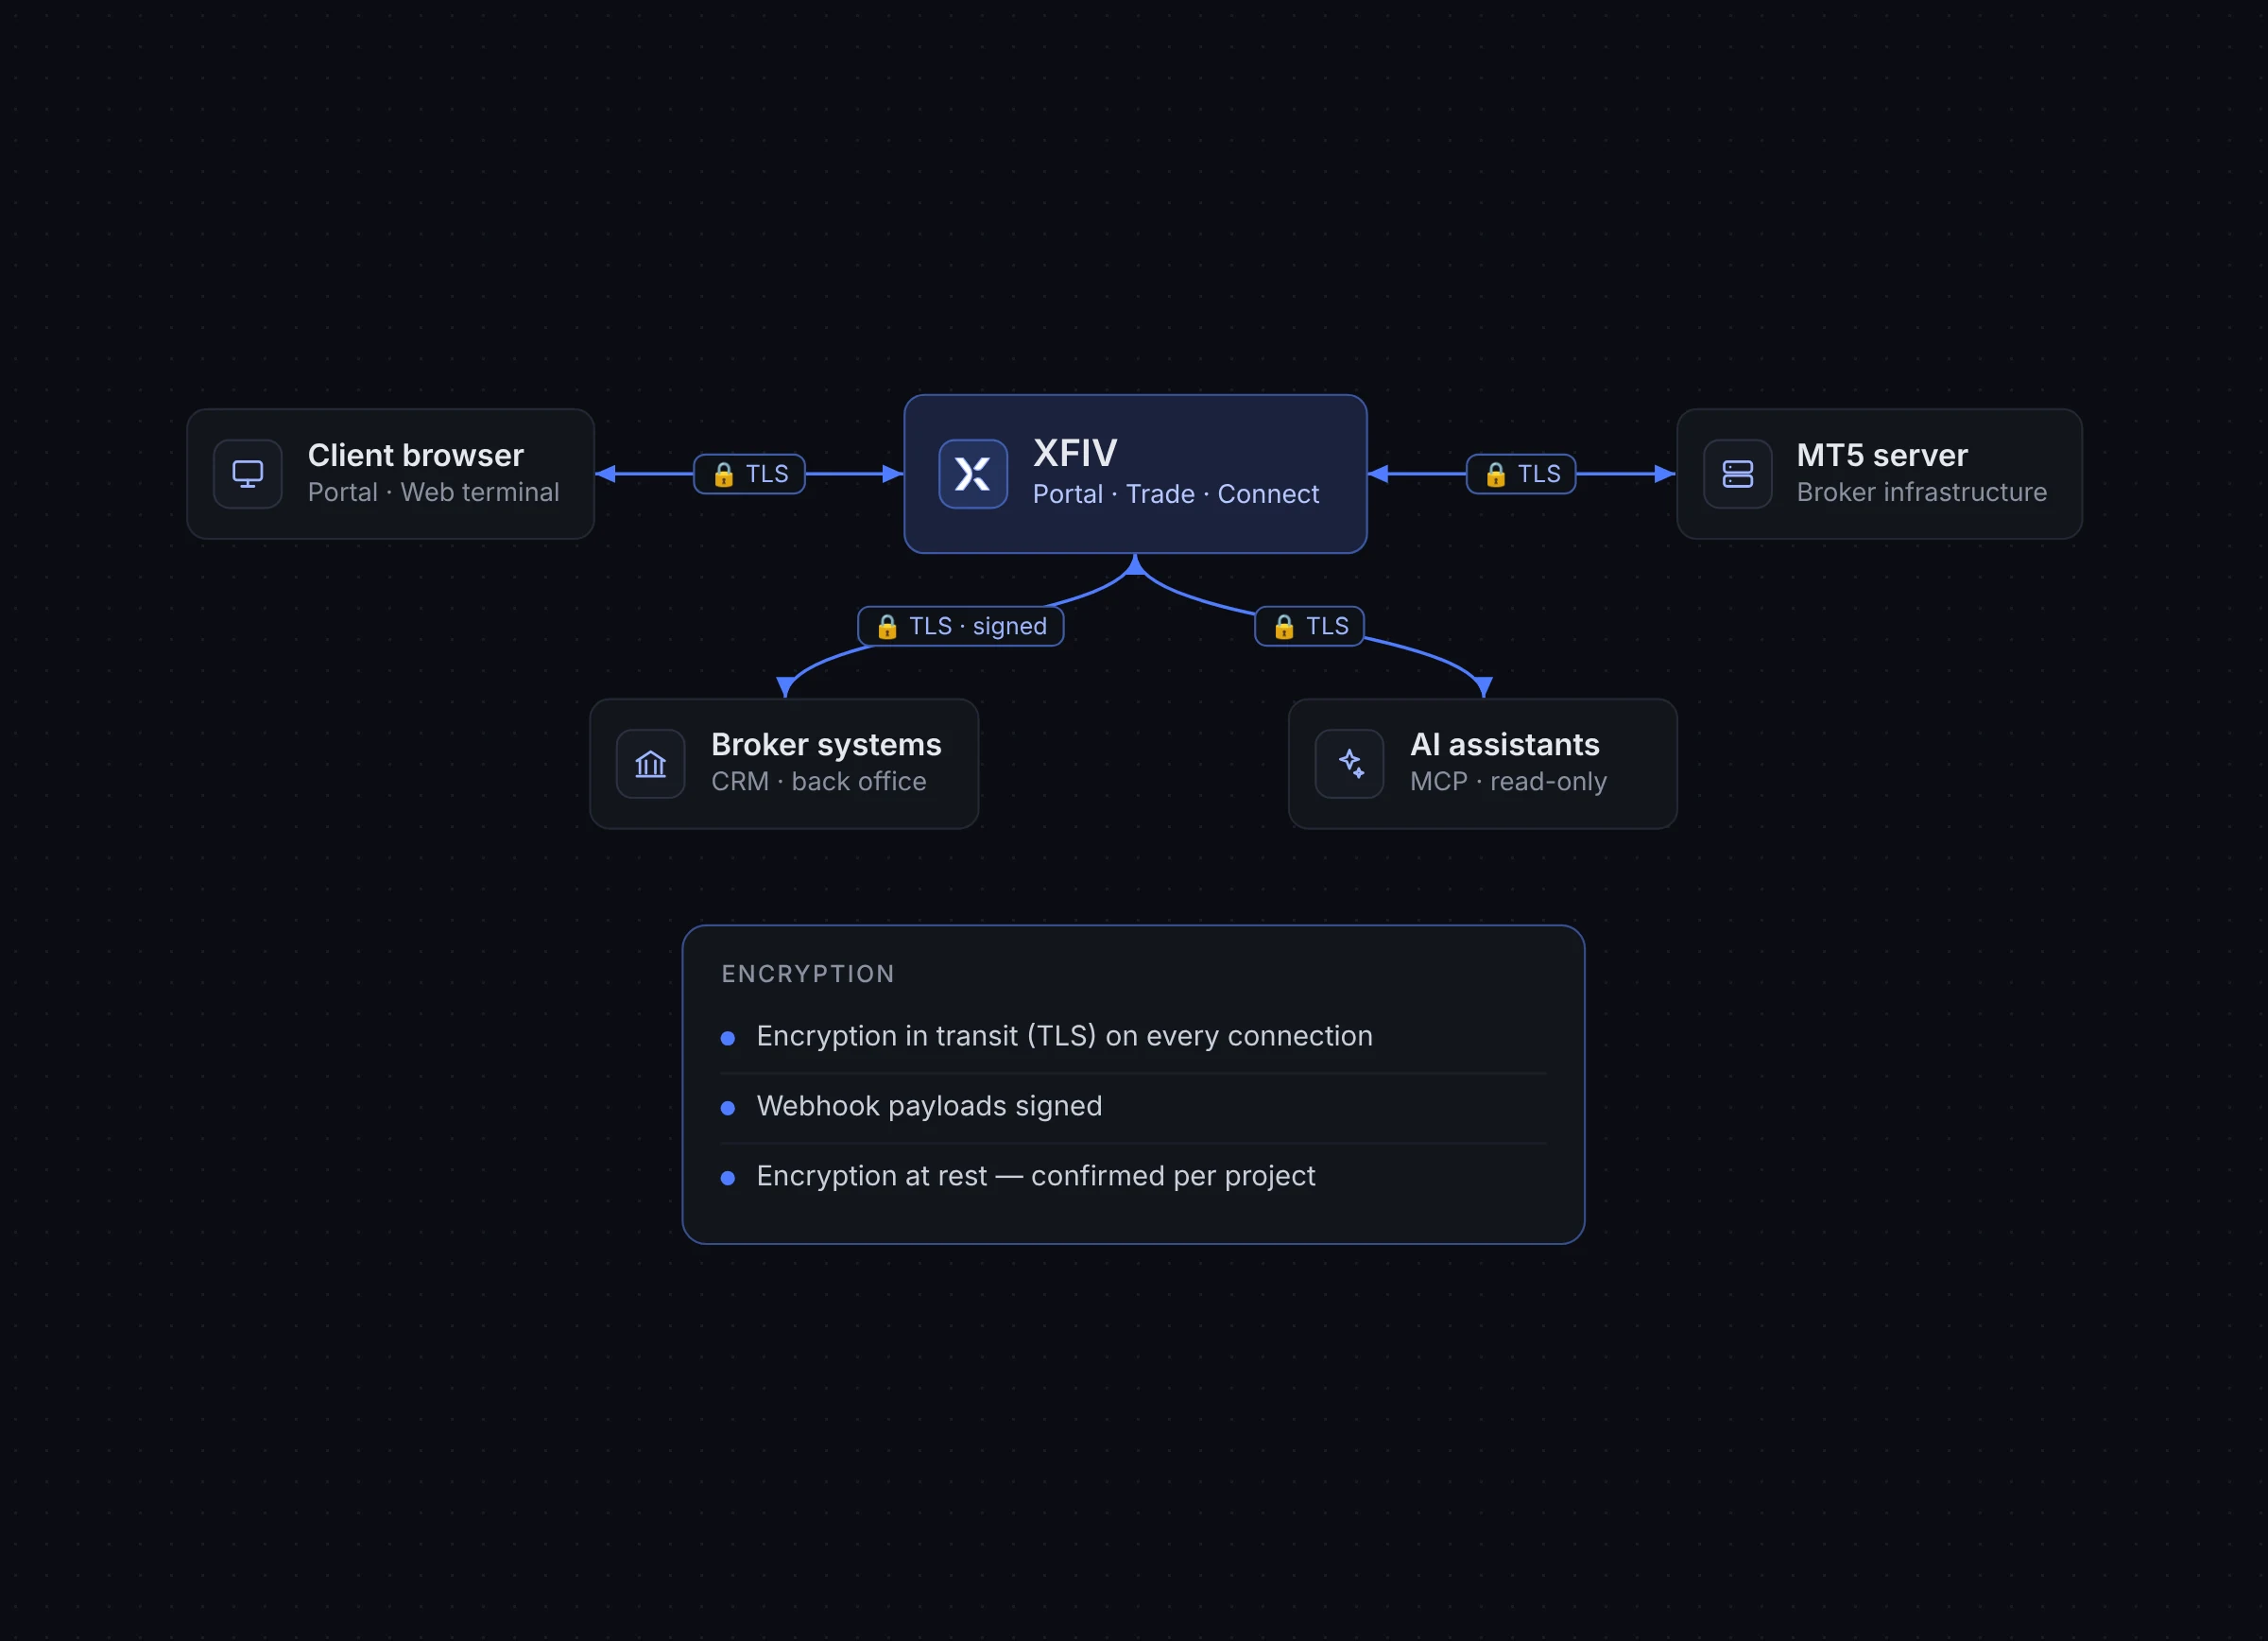
Data moving between clients, brokers and XFIV travels over encrypted connections. Encryption of stored data and backups is confirmed during your security review.

  • Encryption in transit (TLS)
  • Encryption at rest — confirmed per project
Lock icons on data flowing between a client browser, XFIV and an MT5 server
Access control

Least privilege, by default

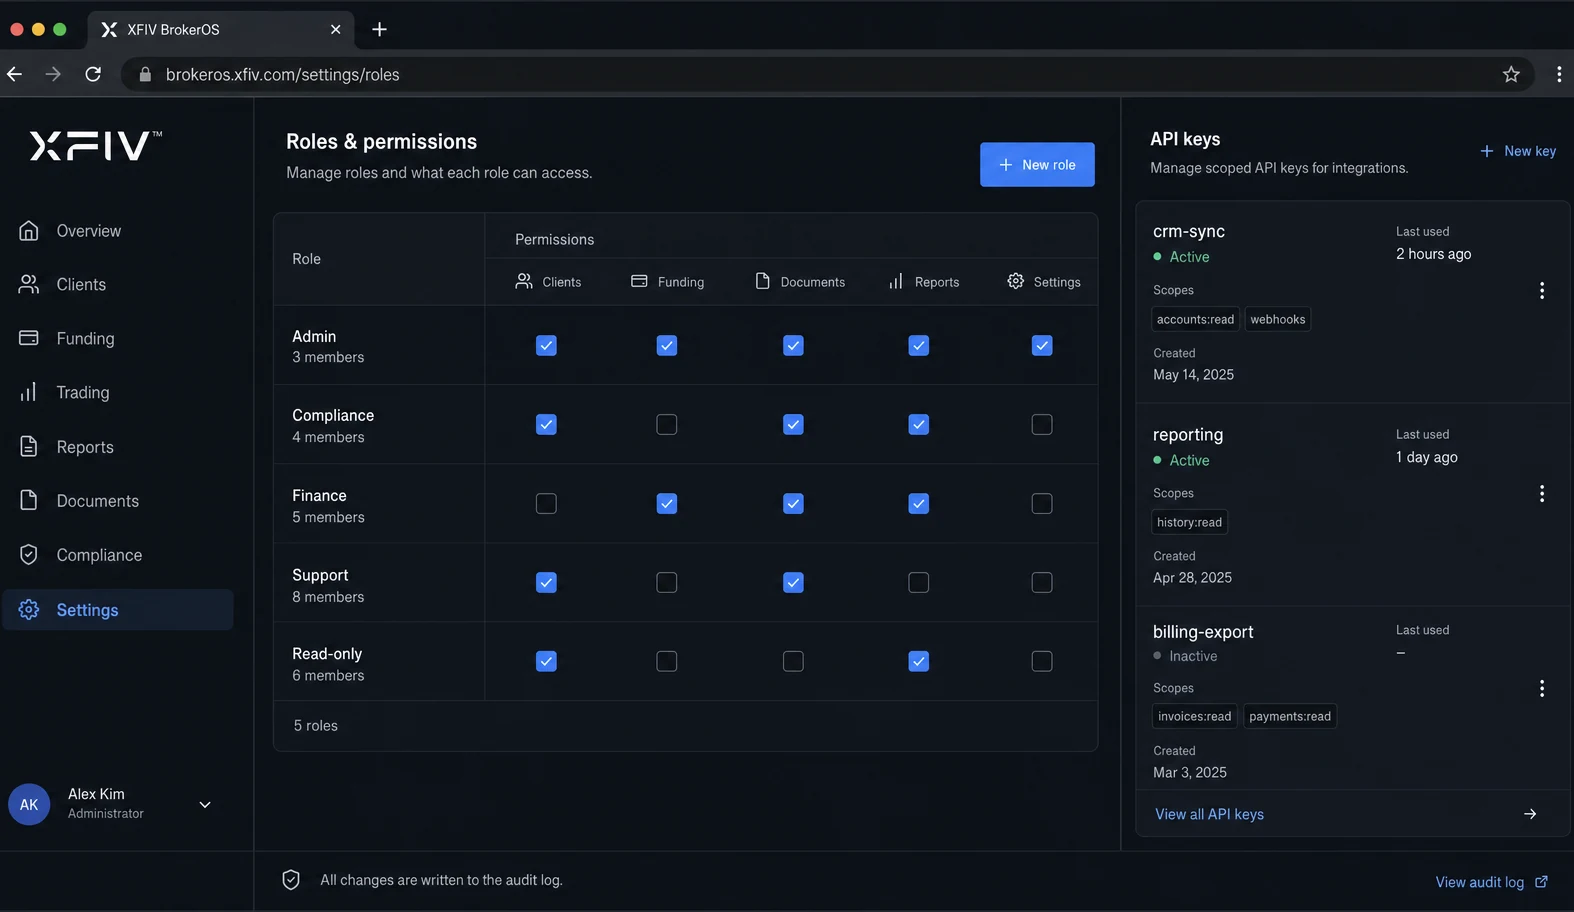
Staff, integrations and AI assistants get only the access they need. Roles control what broker staff can see, API keys are scoped per integration, and every request is logged.

  • Role-based access control
  • Scoped API keys
  • Audit logs for API and MCP requests
Role settings screen assigning permissions to broker staff and API keys
Practices

How we protect broker and client data

Security is a set of habits, not a single feature. These are the practices that apply across XFIV products.

01

Scoped API keys

Each integration gets its own key with only the scopes it needs, so one key can be revoked without affecting others.

02

Signed webhooks

Webhook payloads from XFIV Connect are signed so your systems can check they came from us and were not changed.

03

Rate limits

Limits on API usage protect your MT5 server and our platform from runaway or abusive integrations.

04

Audit logs

A record of who called what, and when, for API calls, MCP requests and staff actions.

05

Logging and monitoring

Service logs help us detect problems early and investigate incidents with facts, not guesses.

06

Sandbox first

Integrations are built and tested against sample data before they touch production accounts.

Certifications

Certifications and assurance

We are building towards formal security certifications. Security questionnaires are answered during onboarding.

Until then, we share how XFIV is designed, what we log and how access is controlled, in writing, as part of your security review. Certifications never replace your own due diligence.

AI and MCP safety

How we keep AI access safe

Two XFIV features give AI models access to account data: the AI agent in XFIV Portal, and the MCP layer in XFIV Connect, which lets clients connect compatible AI assistants to their accounts. Both follow the same rules.

Access is read-only by default. AI assistants and the agent cannot place, modify or close trades. Data scopes are set by the broker and enforced by XFIV Connect, outside the AI model, so a model cannot talk its way past them. Each request is checked against the signed-in client’s own accounts, and every request is written to the audit log.

The agent gives information, not investment advice. When a question needs a person, it hands the conversation to the broker’s support staff. Brokers decide whether to offer AI features at all, to which clients and on which terms.

MCP for Trading Platforms

With XFIV Connect, your clients can link their trading accounts to AI assistants through the Model Context Protocol. Access is read-only by default, scoped by the broker, and every request is logged for review.

Read the MCP guide
MCP
Open standard
Read-only
Default access
Scoped
Permissions set by the broker
Audit Log
Requests logged for review

MCP permissions

Connection

AI assistant (sample)
Account 5012 · via MCP
Active

Permissions

  • Account summaryAllowed
  • Trade historyAllowed
  • Place ordersDisabled
3

Audit log

10:42:07account.summaryallowed
10:42:09history.tradesallowed
10:43:15orders.placeblocked by scope
10:44:02account.summaryallowed

AI responses are informational and are not investment advice.

Shared responsibility

Who is responsible for what

XFIV is a brokerage technology provider, not a broker. Security of a brokerage depends on both of us. This is how responsibilities usually split.

AreaXFIVBroker
Hosting and infrastructureRuns XFIV products on managed cloud infrastructureRuns and secures its own MT5 server
EncryptionEncrypts data in transit; storage encryption confirmed per projectSecures its own systems that receive XFIV data
Access controlProvides roles, scoped API keys and audit logsAssigns roles to staff and reviews access regularly
AI and MCP accessEnforces read-only access and broker-set scopesDecides which scopes and AI clients to allow
IntegrationsSigns webhooks and applies rate limitsVerifies webhook signatures and stores keys securely
RegulationProvides software onlyMeets its own regulatory and legal obligations
Responsible disclosure

Reporting a security issue

If you believe you have found a security vulnerability in an XFIV product or website, please email security@xfiv.com. Include a description of the issue, the steps to reproduce it and any relevant details such as affected pages or requests.

Please give us reasonable time to investigate and fix the issue before sharing it publicly. Do not access, change or delete data that does not belong to you, and do not run tests that could disrupt service for brokers or their clients. We will acknowledge your report and keep you informed as we work on it.

FAQ

Common questions

Where is XFIV hosted?

Hosting details, including region, are confirmed per project and shared during your security review. Sandbox and production are designed to be kept separate.

Is data encrypted?

Data is encrypted in transit. Encryption of stored data and backups is documented for each deployment during your security review.

Does XFIV have ISO/IEC 27001 or SOC 2?

Not yet. We are building towards formal security certifications. Security questionnaires are answered in writing during onboarding.

Can AI assistants trade on client accounts?

No. AI access through XFIV Portal and XFIV Connect is read-only by default, limited to broker-set scopes and logged. AI assistants cannot place trades.

How do I report a vulnerability?

Email security@xfiv.com with a description and steps to reproduce. Please do not disclose the issue publicly until we have had time to fix it.

Planning a security review?

Book a demo and tell us what your review needs. We will answer questionnaires in writing and walk your team through access control, audit logs and AI safety.

Last reviewed 2026-10-29